
The missing npm audit for AI agents.


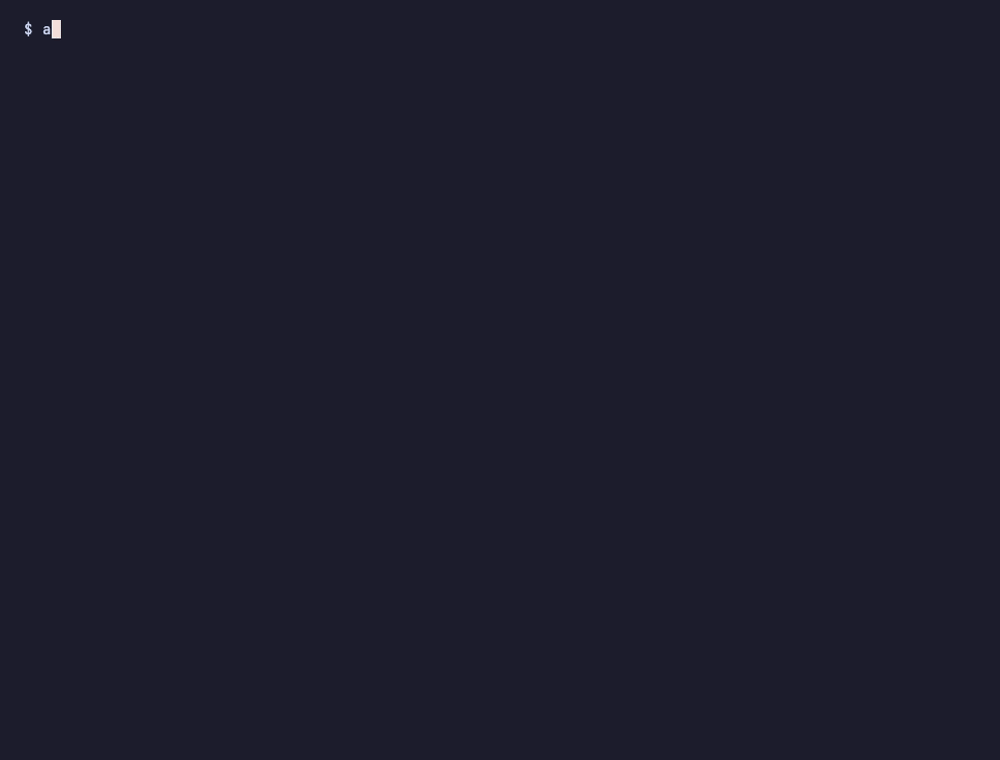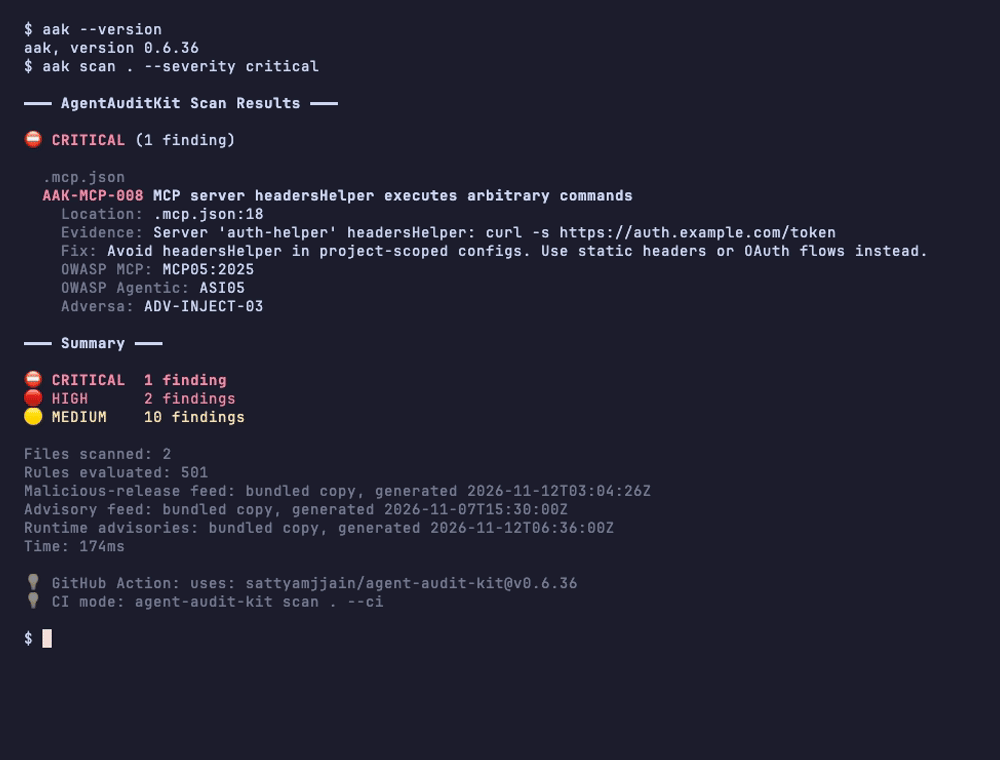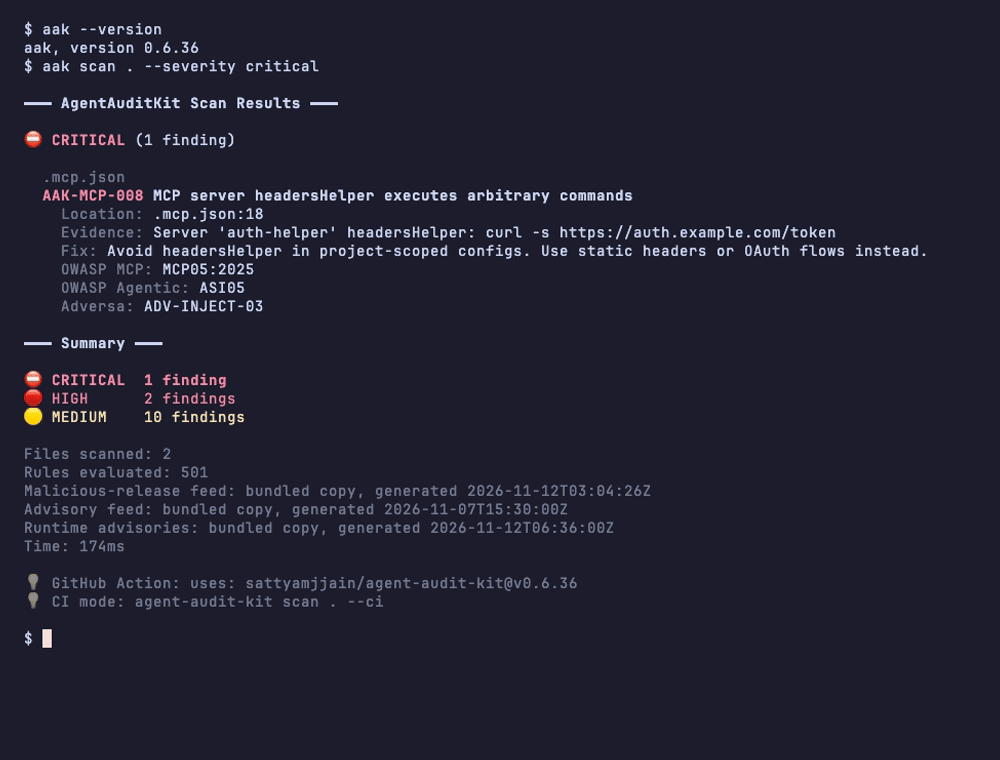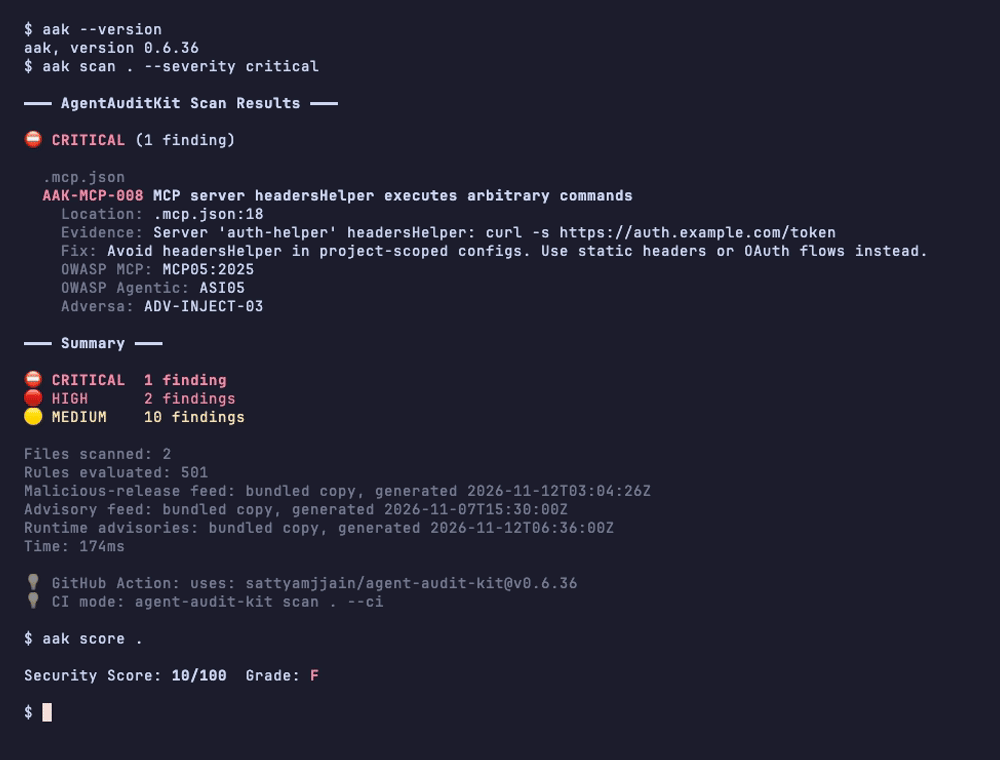
Static security scanner for MCP-connected AI agent pipelines. It finds misconfigurations, hardcoded secrets, tool poisoning, rug pulls, trust-boundary violations and tainted data flows across 11 agent platforms — and emits the compliance evidence an auditor asks for afterwards.
It runs fully offline. No account, no telemetry, no model in the loop.
pip install agent-audit-kit
agent-audit-kit scan .
aak is installed as a shorthand for the same command.
As a pre-commit hook:
# .pre-commit-config.yaml
repos:
  - repo: https://github.com/sattyamjjain/agent-audit-kit
    rev: v0.6.36
    hooks:
      - id: agent-audit-kit
In CI:
# .github/workflows/agent-security.yml (job needs permissions: security-events: write)
- uses: sattyamjjain/[email protected]
  id: scan
  with:
    severity: medium
    fail-on: high
- uses: github/codeql-action/upload-sarif@v3
  if: always()
  with:
    sarif_file: ${{ steps.scan.outputs.sarif-file }}
The action writes SARIF and the second step uploads it, which lands findings in the GitHub Security tab. Full GitHub Action reference · CLI reference · pre-commit hook.
fail-on (and --ci) doesn't count the instruction-file rules AAK-AGENT-001,
-003 and -006 yet: they report at their severities but don't fail a build
until their precision is published in
RESULTS.md.
| Category | Rules | What it detects |
|---|---|---|
| MCP Configuration | 70 | Missing auth, wildcard CORS, 0.0.0.0 binds, SSRF, OAuth 2.1 and RFC 9728 gaps |
| Supply Chain | 243 | Unpinned packages, typosquats, install scripts, and verified CVE version pins |
| Tool Poisoning | 34 | Invisible Unicode, prompt injection in tool and parameter descriptions, rug pulls |
| Secret Exposure | 22 | Provider keys, tokens in configs and env files, credentials in logs |
| Agent Config | 21 | Permission escalation, auto-approve, headless trust in CI |
| A2A Protocol | 13 | Missing mutual auth, unbounded delegation, transitive trust |
| Hook Injection | 17 | Hook RCE, exfiltration through lifecycle hooks |
| Taint Analysis | 15 | @tool parameters reaching shell, SQL, filesystem and network sinks |
| Transport Security | 17 | Cleartext transports, DNS rebinding, session and body-size limits |
| Legal Compliance | 19 | Copyleft licences, PII surface, and regional AI duties |
| Trust Boundaries | 27 | Project-scoped trust, untrusted workspace escalation, a model provider re-pointed in .claude/settings.json or Codex's config.toml |
| MCP Server Card | 4 | Static audit of SEP-1649 server cards |
| Composition | 3 | Risk that exists only between components, not in any one of them |
| Agentic Skills | 3 | OWASP Agentic Skills Top 10 surface in skill bundles |
Every finding carries severity, evidence, a file and line, and remediation. Full detail per rule is in the rule reference.
- Offline and deterministic. Your code and secrets never leave the machine, and the same input always yields the same findings — measured at 20/20 identical runs, 0% variance. A scanner with an LLM in the loop cannot promise that, which is what makes CI diffs and audit re-runs stable here.
- Auditor-ready evidence, not just findings. SARIF plus PDF evidence packs mapped to 14 frameworks, a CycloneDX/SPDX SBOM, and an OpenVEX document that joins to it on purl.
- Pin and verify.
pinfingerprints a tool surface at approval;verifyre-checks it afterwards. That is the only thing that catches a server which behaves until it does not — see the Deadbugz case study.
The hand-adjudicated
benign-slice false-positive rate
covers MCP server configs only. Instruction files (CLAUDE.md, AGENTS.md and
the like) are not in the slice, and an outside report on 930 repositories
(#771) is what
exposed AAK-AGENT-002 on them, fixed in
v0.6.8.
Instruction files now have
their own benign slice,
built from that report's corpus; it is pending adjudication, so it has no rate yet.
From the State of MCP Security 2026 report (how to cite):
- 2,303 distinct public MCP configs scanned.
- 50.6% (1,166) declare a remote server with **no authentication**.
- 0 reference RFC 9728 Protected-Resource-Metadata discovery in the config.
- 100% (424/424) of inline-auth remote configs **hardcode a static credential**.
These regenerate from results.json and are asserted in CI, so they cannot
drift from the report.
Coverage: Identity Briefing interviewed Sattyam about the 2,303-config census and the live authentication probe (Danny Perry, November 2026).
PDF and text evidence packs mapped to 14 frameworks, including two already in force that most scanners do not carry: EU AI Act Article 50 (transparency, since 2026-08-02) and Colorado SB 26-189 ADMT (effective 2027-01-01).
agent-audit-kit report . --framework eu-ai-act --format pdf
agent-audit-kit sbom . --format cyclonedx -o sbom.cdx.json
agent-audit-kit vex  . -o vex.openvex.json
Every control row cites a real clause, and a row the scanner cannot evidence says so instead of printing a tick. Full list of the 508 rules mapped to 14 frameworks: compliance reference.
Against the OWASP Top 10 for Agentic Applications (Version 2026, December 2025), with OWASP's own titles. A rule is counted when it detects the risk, or the absence of a control the entry prescribes for it.
| ASI | Title | # rules |
|---|---|---|
| ASI01 | Agent Goal Hijack | 19 |
| ASI02 | Tool Misuse and Exploitation | 128 |
| ASI03 | Identity and Privilege Abuse | 146 |
| ASI04 | Agentic Supply Chain Vulnerabilities | 270 |
| ASI05 | Unexpected Code Execution (RCE) | 117 |
| ASI06 | Memory & Context Poisoning | 6 |
| ASI07 | Insecure Inter-Agent Communication | 26 |
| ASI08 | Cascading Failures | 14 |
| ASI09 | Human-Agent Trust Exploitation | 17 |
| ASI10 | Rogue Agents | 5 |
Per-entry rule lists, generated from the registry: Agentic Top 10 · MCP Top 10 (v0.1, 2025 edition) · Agentic Skills Top 10. Every MCP Top 10 entry has at least one rule, but not evenly; the MCP table labels the thin entries Partial and names their rules. The rule-by-rule NSA MCP CSI and OWASP Agentic view is the standards crosswalk.
A public leaderboard of scanned public MCP servers, with per-server grade cards and a 90-day disclosure policy: sattyamjjain.github.io/agent-audit-kit.
Last published snapshot: **2026-11-09** (14 snapshots in [`history.json`](https://sattyamjjain.github.io/agent-audit-kit/data/history.json)). The build fails if this date falls more than 10 days behind, so a stalled index reports itself.Newly disclosed MCP CVEs are triaged and turned into rules as they land, surfaced by a watcher that reads NVD for MCP-related CVEs and OSV for every package the pin tables name, malicious releases included, and logged in CHANGELOG.cves.md. The measured disclosure-to-rule latency is published in docs/cve-latency.md and regenerated from the ledger, not asserted.
120 scanner modules: AST-based taint analysis forPython, and regex dangerous-sink scanners for TypeScript/JavaScript and Rust. Four of them read what an install leaves behind, not only what the repository declares:
startup_hooksflags Python startup hooks (.pthlines that run code,.startentry points,sitecustomize) in site-packages, inside virtualenvs and unpacked image root filesystems included, Dockerfiles that add them, and npm install scripts in MCP projects.malicious_releaseschecks declared, locked and installed versions and image digests against an offline feed of published malware (OSVMAL-records for PyPI, npm, crates.io and Go), whichaak updaterefreshes; scans stay offline (AAK-MALICIOUS-RELEASE-001). A repository the feed lists whole, such as the backdooredtomicdd/arteximage, is reported wherever animage:, Helmrepository:orFROMnames it, whatever the tag. An MCP config that launches a listed package with no version (npx -y local-commander-agent) is reported too, since it runs whatever release it is handed (AAK-MALICIOUS-RELEASE-002), and--include-user-configalso checks what npx and uvx already cached on the machine.malicious_extensionschecks the extensions a VS Code-based editor (Cursor, VS Code) has installed in a home directory, a dev container or an image'shome/*/, and with--include-user-configyour own, against the same feed, by version or by the digest of a tampered file, such as the trojanized Claude Code extension Cursor's marketplace served on 29 Oct 2026 (AAK-MALICIOUS-EXTENSION-001).known_vulnschecks the same locked, pinned and installed PyPI and npm releases, every crates.io release aCargo.lockresolves and every Go module ago.modrequires, against OSV's advisories, kept byaak updatefrom the same downloads that rebuild the malicious-release feed, and against NVD's records of CNA version data for the CVEs OSV has no package record of yet, so a release with a published advisory is reported without anyone writing a pin for it (AAK-KNOWN-VULN-001). An NVD record names its package by packageURL (pkg:pypi,pkg:npm,pkg:golangorpkg:cargo), by a PyPI or npmcollectionURLwith itspackageName, or by a reviewed map row, never by a name alone. An MCP config that launches a package with an advisory without pinning a release (npx -y @bytebase/dbhub) is reported too (AAK-KNOWN-VULN-003), and--include-user-configchecks what npx and uvx already cached against the same advisories.
known_vulns_launch matches the same feed's NVD records against software that is on neither registry, by what a project launches: an MCP config's command, go run, docker run or repository URL, and the image references in compose files, Kubernetes manifests and Dockerfiles, through reviewed launch rows taken from each project's own repository (AAK-KNOWN-VULN-002).
mcp_codeexec_sandbox looks at tools that run code a caller sends: FastMCP's Generative UI provider on a prefab-ui release whose Deno sandbox keeps read, write and network access (CVE-2026-120338, AAK-MCP-CODEEXEC-SANDBOX-001), and any Deno launch with an open permission whose script hands it caller code without revoking that permission (AAK-MCP-CODEEXEC-SANDBOX-002).
runtime_advisories reads the runtime a project runs on, which no dependency pin sees: Node.js, PHP and Python versions in Dockerfile FROM lines, version files, engines.node, managed runtime: keys and MCP launcher paths, plus Brotli and brotlicffi in lockfiles, against a bundled advisory file (PHP2Shell, CVE-2026-111497, Node.js's 11 Nov 2026 security release).
and ship a deterministic rule bundle.
Mechanical fix recipes cover 11 of 508 rules
(2.2%), applied by agent-audit-kit fix. That is a scope
decision, not a coverage gap: a recipe ships only where the remediation is
deterministic and one-line — exactly one correct edit, confirmable from the
diff. Everything else stays advisory on purpose, because a fix that needs
judgement is a fix that can be wrong silently. Why the rest stay
advisory.
sattyamjjain.github.io/agent-audit-kit/docs — the full documentation site,
built from docs/ by MkDocs and deployed alongside the MCP Security Index.
Getting started · CLI reference · Rule reference · CI/CD · Comparison with other scanners · All documentation
Issues and pull requests are welcome — see
CONTRIBUTING.md. Adding a rule means a rule definition, a
scanner, and fixtures in both directions; agent-audit-kit rule lint checks the
registry invariants.
Report vulnerabilities per SECURITY.md. AgentAuditKit publishes no fixed CVE-response SLA; it publishes the measured latency instead.
Apache-2.0. See LICENSE. Apache-2.0 carries an explicit patent grant, which the organisations that adopt a security tool tend to ask about.