Repository navigation
Requirements: update django-allauth - #9249
Conversation


|
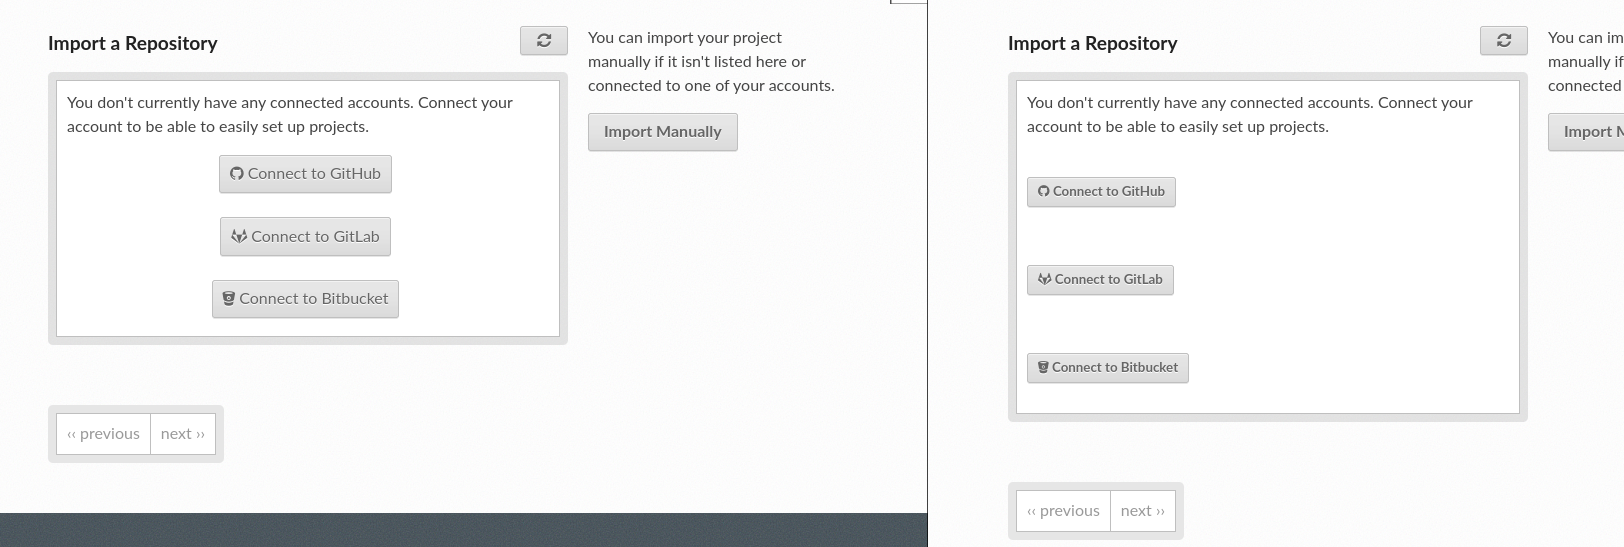
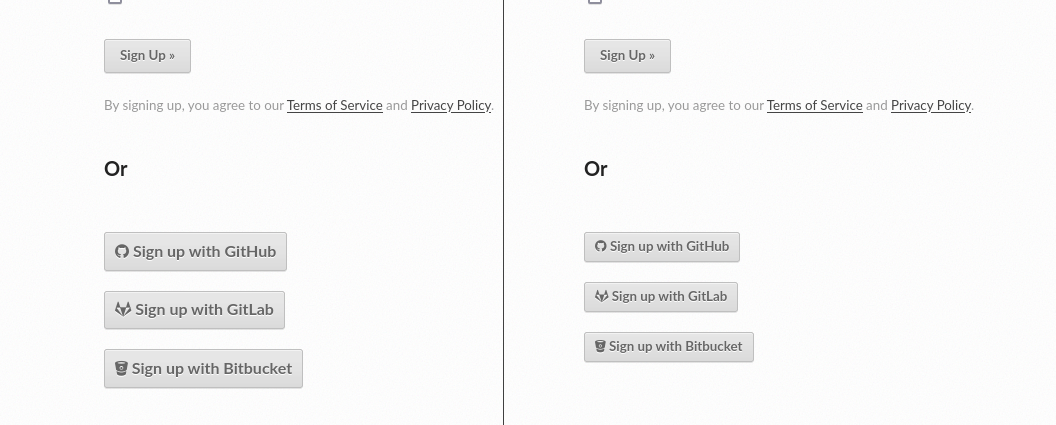
This is how it looks like with the changes :/
|

\### 0.43.0

> In previous versions, the allauth app included a base.html template. This
> template could conflict with an equally named template at project level.
> Therefore, base.html has now been moved to account/base.html -- you will need
> to check your templates and likely override account/base.html within your
> project.

We include our own base.html template,
in order to make the allauth templates
use our base template I have added a an account/base.html
file that just extends from base.html.

\### 0.44.0

> The certificate key part of the SOCIALACCOUNT_PROVIDERS configuration has been
> renamed to certificate_key. This is done to prevent the key from being
> displayed without being masked in Django debug pages.

We don't use that field nor we access it from our application.

\### 0.47.0

> Added a new setting SOCIALACCOUNT_LOGIN_ON_GET that controls whether or not the
> endpoints for initiating a social login (for example,
> "/accounts/google/login/") require a POST request to initiate the handshake. As
> requiring a POST is more secure, the default of this new setting is False.

This adds one more step for users before signing in with an external provider.

> You are about to sign in using a third party account from GitHub.
> [ Continue ]

I have changed our list to be a form,
so it stil is just a click away from our platform,
but a link from outside will require the user to click on "continue".
We can just set this setting to True if we want too
(but there is a security notice that explains why isn't a good idea https://github.com/pennersr/django-allauth/blob/master/ChangeLog.rst#security-notice)

\### 0.48.0

> The newly introduced ACCOUNT_PREVENT_ENUMERATION defaults to True impacting the
> current behavior of the password reset flow.

We want that.

> The newly introduced rate limitting is by default turned on. You will need to
> provide a 429.html template.

We want this, I have added a 429.html template :)

> The default of SOCIALACCOUNT_STORE_TOKENS has been changed to False. Rationale
> is that storing sensitive information should be opt in, not opt out. If you
> were relying on this functionality without having it explicitly turned on,
> please add it to your settings.py.

We rely on this, I have set it to true.

\### 0.49.0

> Changed naming of internal_reset_url_key attribute in
> allauth.account.views.PasswordResetFromKeyView to reset_url_key.

We don't override this view.
21250a5 to
d10984e
Compare

|
The new settings are working as expected locally with ngrok :) |

|
@stsewd is this PR waiting on frontend fixes? |

|
The import page definitely needs a fix, that doesn't look great. The padding on the buttons isn't a big deal, but should also be an easy fix. |
yeah, just the CSS part is missing, it also needs to be fixed on .com. We could also leave it as before, but users will need to press another button to connect their account
currently this is done in a single click |
|
My instance isn't booting, so can't test anything at the moment. But the issue is that |
|
Also, I assume https://readthedocs.org/accounts/social/connections/ is likely affected too, as it also uses |

 agjohnson
left a comment
agjohnson
left a comment
There was a problem hiding this comment.
The changes included here so far look good, but the styles on at least li > form > button need fixed to merge this.
|
This is how it looks like on the connected services page
I'm testing this again and wasn't able to replicate the look of the first picture anymore (tested with firefox and chrome this time)...
The only visual change overall is that the buttons are smaller |


|
Yeah, padding and text size both look smaller. That should be an easy fix though. |
|
Just to clarify, I'm not actively working on this. I'm happy to review this however and happy to answer any specific questions on the styles or CSS that come up. |
|
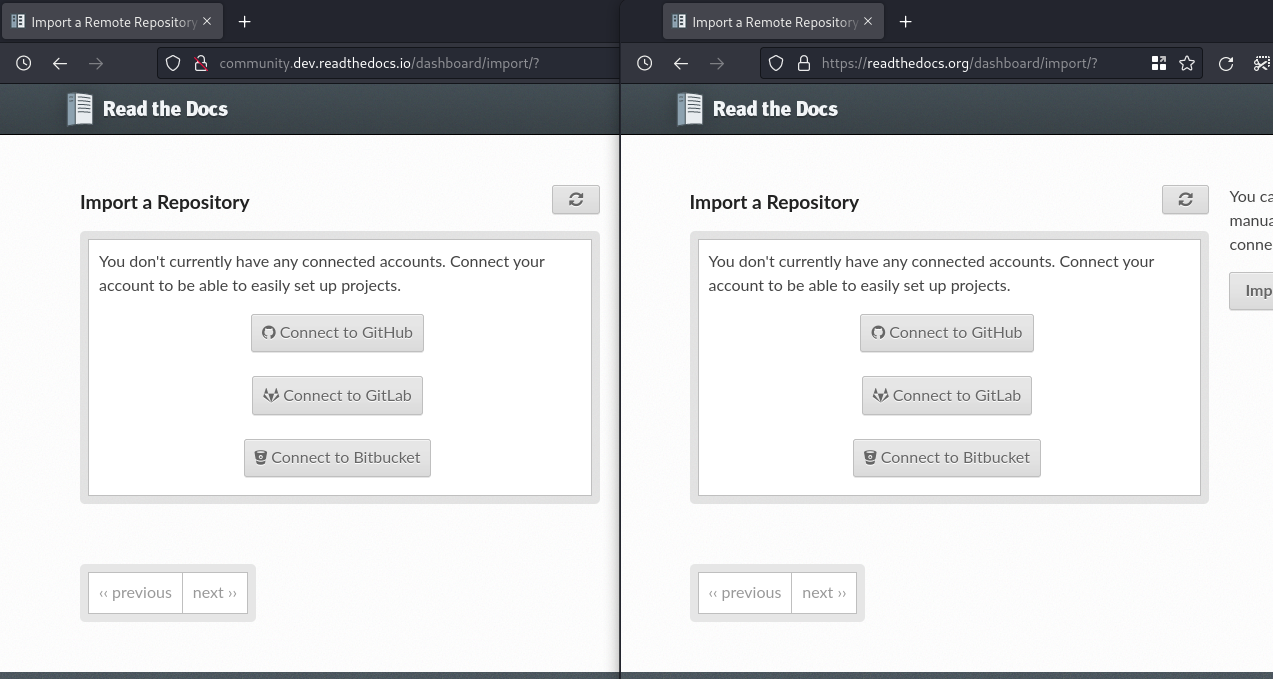
OK, I think I was able to fix this, mainly just took the old values and put them on a new rule. Find the differences:
|



 humitos
left a comment
humitos
left a comment
There was a problem hiding this comment.
Looks good to me!
Do we need to care about any kind of data migration of similar?
agjohnson
left a comment
agjohnson
left a comment
There was a problem hiding this comment.
CSS changes look good!
Nope, nothing has changed on the models |
|
There is a PR on .com that we need to merge too |


0.43.0
We include our own base.html template,
in order to make the allauth templates
use our base template I have added an account/base.html
file that just extends from base.html.
0.44.0
We don't use that field, nor we access it from our application.
0.47.0
This adds one more step for users before signing in with an external provider.
I have changed our list of links to be a form,
so it still is just a click away inside our platform,
but a link from outside will require the user to click on "continue".
We can just set this setting to True if we want too,
but there is a security notice that explains why isn't a good idea https://github.com/pennersr/django-allauth/blob/master/ChangeLog.rst#security-notice.
We need to update the CSS from .com too, and I may need help with the .org CSS..
0.48.0
We want that.
We want this, I have added a 429.html template :)
We rely on this, I have set it to true.
0.49.0
We don't override this view.
Closes #9122