

Enterprise Code Quality and Security Analysis
SonarSource (sonarsource.com) is the company behind SonarQube, SonarQube Cloud (formerly SonarCloud), and SonarLint — the most widely adopted suite of static code analysis and security scanning tools in software development. SonarQube analyzes code for bugs, vulnerabilities, code smells, and security hotspots across 30+ programming languages, integrating directly into CI/CD pipelines and pull request workflows. Trusted by 7M+ developers at organizations including Snowflake, Deutsche Bank, and Booking.com.
How SonarSource Works
SonarQube Cloud connects to your GitHub, GitLab, Bitbucket, or Azure DevOps repository and analyzes every pull request and merge automatically. It identifies bugs, security vulnerabilities, code duplication, and coverage gaps — then provides actionable feedback with AI-driven fix suggestions directly in the PR interface. Quality gates block merges when code fails defined thresholds. SonarLint brings the same analysis into the IDE in real time, so developers catch issues before they commit. SonarQube Server (self-managed) is available for teams requiring on-premises deployment.
Key Features
- Static code analysis (SAST) — detects bugs, vulnerabilities, and code smells across 30+ languages
- AI code verification — reviews AI-generated code for security and quality issues before merge
- Pull request analysis — automatic inline feedback on every PR with AI-powered fix suggestions
- Quality gates — block merges failing defined security and quality thresholds
- SonarLint IDE plugin — real-time analysis in VS Code, IntelliJ, Eclipse, and Visual Studio
- SCA scanning — identifies vulnerabilities in open source dependencies
- Branch analysis — track code quality across all active branches
- 30+ language support — Java, Python, JavaScript, TypeScript, C, C++, C#, Go, PHP, and more
SonarSource Pricing
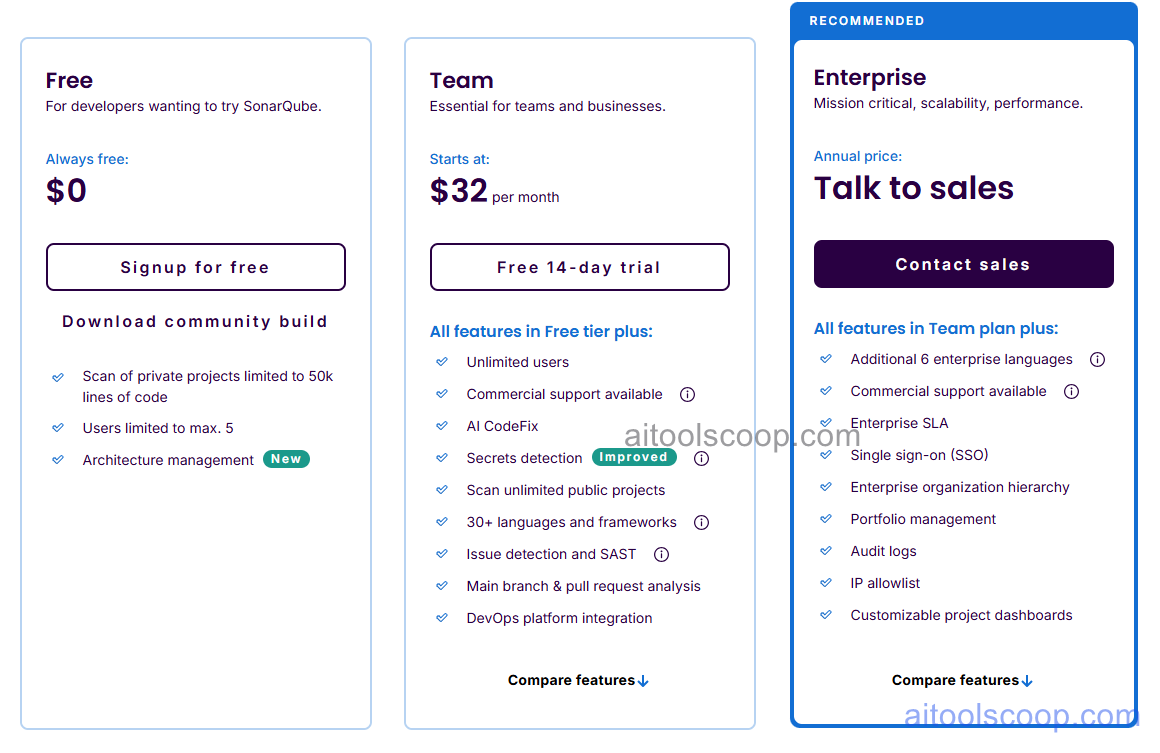
- Free — $0/month — SonarQube Cloud Free tier up to 50K lines of code for private projects; unlimited for open source public projects.
- Team — $32/month — SonarQube Cloud Team plan, up to 100K lines of code for private projects, advanced analysis features, pull request decoration, and branch analysis. Scales by LOC volume.
- Enterprise — Custom pricing — unlimited LOC, enterprise-grade hierarchy, advanced SAST, SCA, SSO, and commercial support. Annual only.
SonarQube Server (self-managed) is priced separately per instance per year based on lines of code. Community Edition is free and open source.
Always check the latest rates on the official website. For more AI tool reviews, visit aitoolscoop.com.
Who Should Use SonarSource?
SonarSource is the default choice for engineering teams that need a proven, enterprise-grade code quality platform with broad language support and deep CI/CD integration. The free Community Edition and SonarQube Cloud free tier suit individual developers and small open-source teams. The Team plan suits growing commercial teams needing PR analysis and quality gates. Enterprise and self-managed deployments serve regulated industries and large organizations with complex compliance requirements.


